H3n Brandmark h3n-x
ES
Available for projects
Colombia

Henry Pacheco (H3n)

Linux & Backend Developer

Specialized in Linux systems, Bash automation, and Python backend services. Focused on predictable code, system hardening, and tooling that solves real operational challenges.

Explore Projects Download Resume (PDF) GitHub LinkedIn

About Me

I started in software development by exploring the internals of Linux operating systems and shell automation. That drive to understand how systems function underneath the abstraction layer guided me toward Unix administration and resilient backend services.

I am currently pursuing a university degree in Systems Engineering while continuously advancing in infrastructure security and system hardening. My engineering mindset prioritizes simplicity, operational predictability, and code supported by clear documentation.

Core Specialties & Focus

  • Linux operating systems, process management, and CLI tooling
  • Modular automation & idempotent shell scripting with Bash
  • Python backend services and REST API architectures

Featured Projects

5 Case Studies

Comprehensive defense in depth: code auditing, container isolation, host hardening, and attack surface management

Click any project to inspect its underlying architecture, engineering decisions, and security benchmarks.
Systems & Automation v0.3.0 · Active Maintenance & Semantic Releases
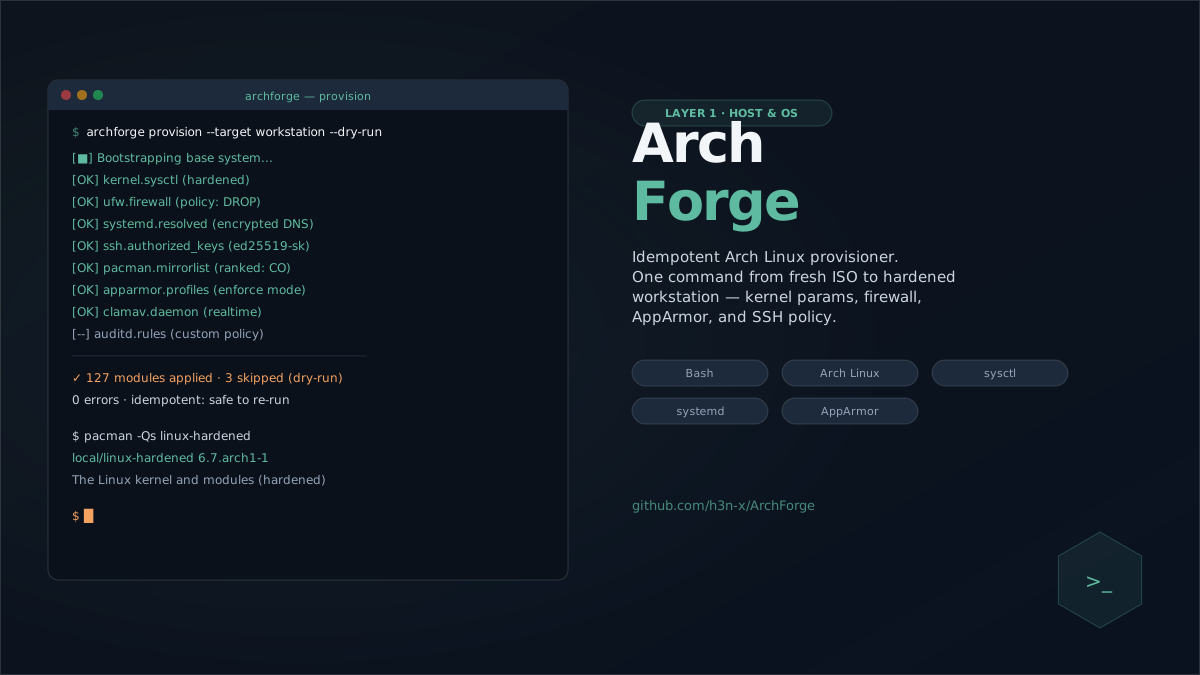
Demostración técnica de ArchForge
Explore Case Study

ArchForge

Modular post-installation & hardening toolkit for Arch Linux
Bash Arch Linux systemd nftables +2
Backend & Security v0.2.0 · 91% Cov · 0 CVEs & CI/CD Hardened
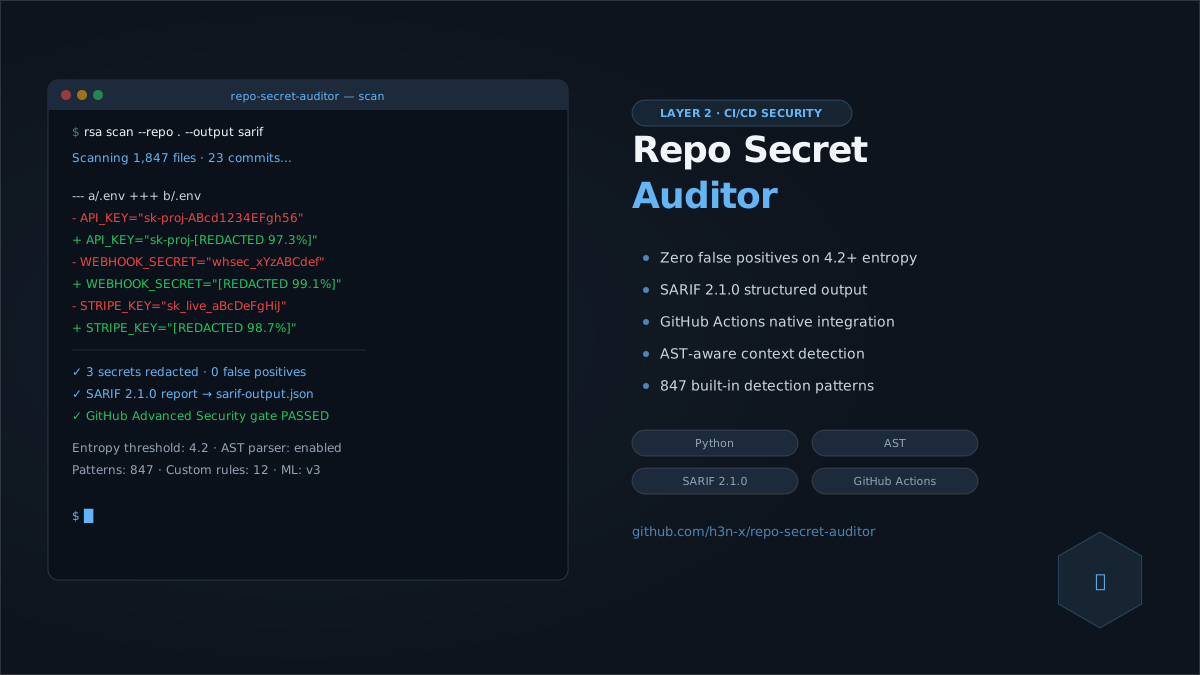
Demostración técnica de Repo Secret Auditor
Explore Case Study

Repo Secret Auditor

Backend secret & dependency scanner engine with native SARIF 2.1.0 integration
Python FastAPI Gitleaks TOML OSV Batch API +5
Containers & Runtime v0.1.0 · 71 Tests (100% rules cov) · Active Release
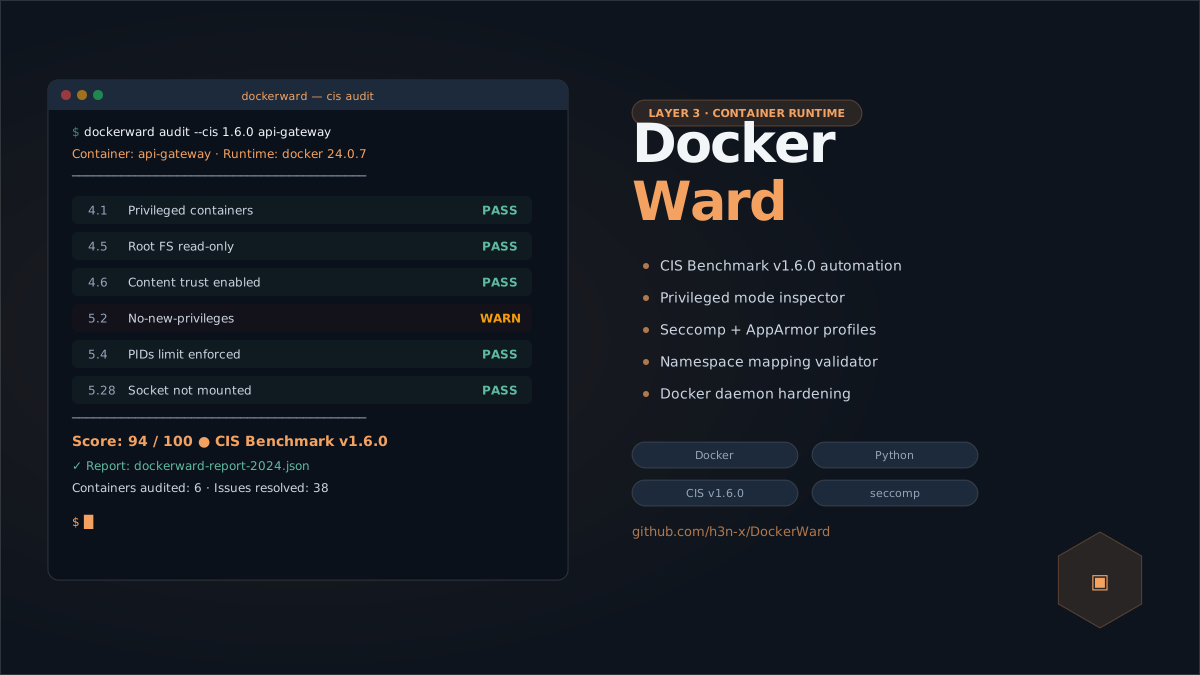
Demostración técnica de DockerWard
Explore Case Study

DockerWard

Runtime container security auditing engine for Docker with native SARIF 2.1.0 reporting
Python 3.12+ Docker Engine API Linux Kernel SARIF 2.1.0 +3
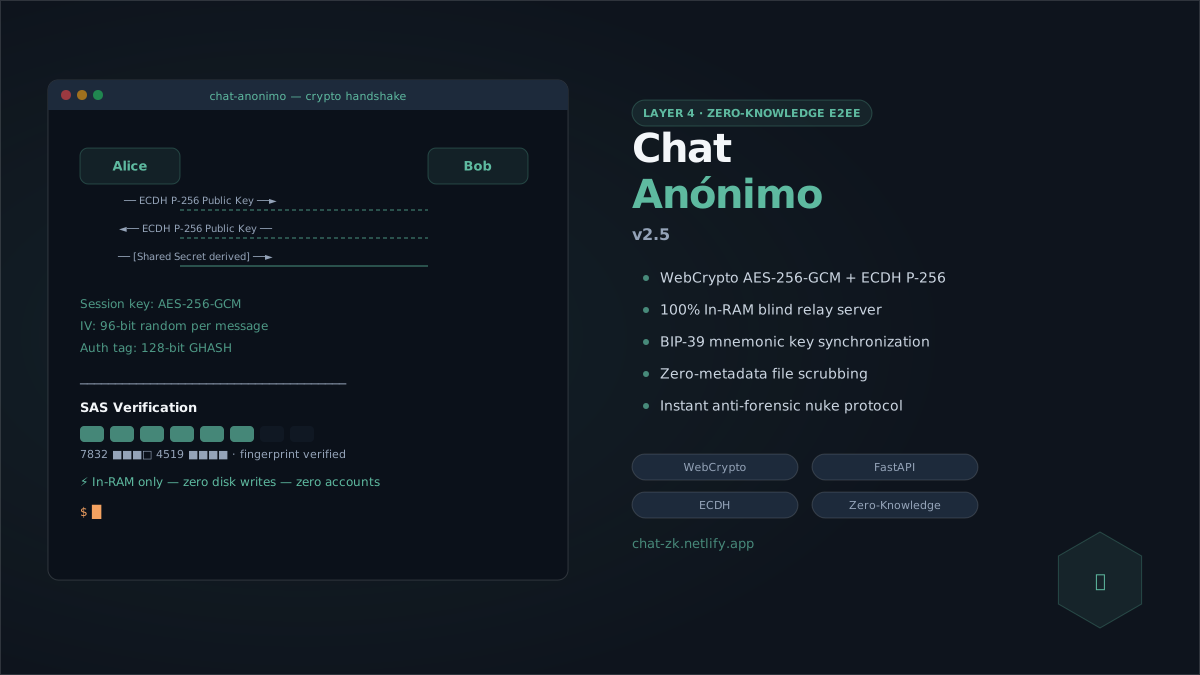
Cryptography & Anti-Surveillance v2.5.0 · 28 Pytest Tests · 12 Vitest Tests · Zero-Persistence RAM
Demostración técnica de Chat Anónimo v2.5 — Privacy & Anti-Surveillance Suite
Explore Case Study

Chat Anónimo v2.5 — Privacy & Anti-Surveillance Suite

Military-grade ephemeral messaging suite with native Zero-Knowledge Blind Relay, biometric voice scrambling, LSB steganography, and Android app with FLAG_SECURE
WebCrypto API (AES-256-GCM) ECDH (P-256) & HKDF Web Audio API (Voice Scrambler) LSB Image Steganography +8
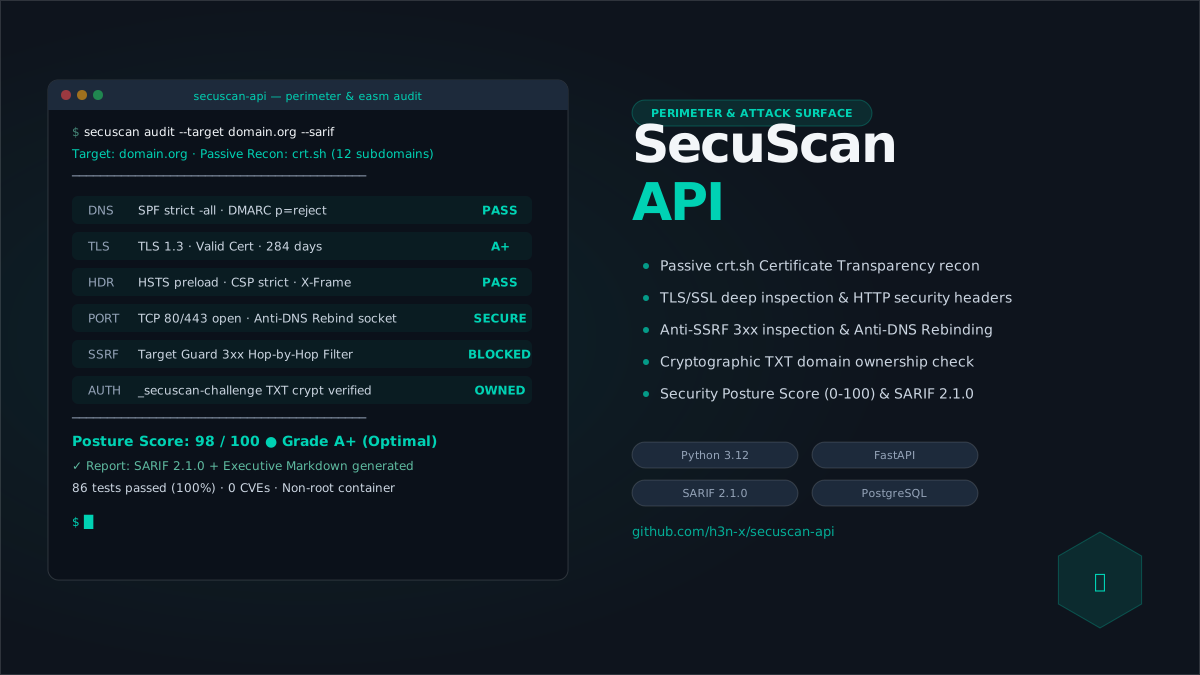
Perimeter & EASM v0.1.0 · 86 Tests (100%) · 0 CVEs · Hardened Non-Root
Demostración técnica de SecuScan API
Explore Case Study

SecuScan API

High-performance backend API for perimeter security auditing and External Attack Surface Management (EASM)

Python 3.12 FastAPI EASM & DNS Security TLS/SSL Deep Inspection +5
Systems & Automation v0.3.0 · Active Maintenance & Semantic Releases

Modular post-installation & hardening toolkit for Arch Linux

Demostración técnica de ArchForge

Problem Statement

Setting up a clean Arch Linux workstation manually takes hours of error-prone configuration steps, frequently leading to environment drift, insecure firewall presets, and forgotten system daemons.

Key Architecture Decisions

  • • Domain-driven modularity: decoupled modules for system security, networking, power management, graphics, and core CLI utilities.
  • • Safe dry-run execution: inspect commands and planned operations prior to applying any changes to the host operating system.
  • • Session-based automatic backups: safeguards existing dotfiles and /etc configuration files before altering files.
  • • Predictable logging & error handling: standardized exit codes and audit trails for reliable operations.

Technical Challenges & Learnings

  • • Idempotent shell scripting patterns designed to run repeatedly without mutating valid system state.
  • • In-depth systemd service orchestration, daemon supervision, and firewall rule syntax with nftables.
  • • Enforcing disciplined semantic versioning and detailed changelogs for systems tooling.
Technologies:
Bash Arch Linux systemd nftables Linux CLI Git
Backend & Security v0.2.0 · 91% Cov · 0 CVEs & CI/CD Hardened

Backend secret & dependency scanner engine with native SARIF 2.1.0 integration

Demostración técnica de Repo Secret Auditor

Problem Statement

Accidental credential leakage (API keys, private tokens, certificates) and stale dependencies in Git repositories are leading attack vectors. Teams frequently lack lightweight, self-hosted audit runners that integrate into CI/CD pipelines without incurring costly enterprise SaaS overhead.

Key Architecture Decisions

  • • Gitleaks-compatible TOML rule engine combined with Shannon entropy filtering and heuristic keyword checks to eliminate false positives.
  • • Deep Git history commit scanner (`--history`) analyzing added diffs (`git log -p`) to catch credentials introduced and deleted across past revisions with commit SHA and author attribution.
  • • Granular baseline suppression framework (`.rsa-baseline.json`) suppressing accepted risks by evidence hash with optional expiration date checking.
  • • Enterprise CycloneDX 1.5 JSON Software Bill of Materials (SBOM) exporter embedding standard Package URLs (PURL) for PyPI and npm ecosystems.
  • • Multi-ecosystem dependency auditor supporting `poetry.lock`, `pyproject.toml` (PEP 621), `requirements.txt` (version ranges) and `package-lock.json` querying the OSV Batch API (`/v1/querybatch`).
  • • FIRST.org compliant CVSS v3.1 vector calculator parsing raw metric strings into exact numerical base scores (e.g. 9.8), preventing silent CI gate bypasses.
  • • Native OASIS SARIF 2.1.0 exporter populating findings directly into GitHub Code Scanning, accompanied by a reusable GitHub Actions workflow with strict HIGH/CRITICAL failure policies.
  • • Comprehensive defensive hardening: rigorous anti-SSRF enforcement (blocking private IP ranges and cloud metadata), Git ref flag injection mitigation, and `SensitiveDataFilter` logging protection.

Technical Challenges & Learnings

  • • Designing modular static analysis engines capable of dual execution modes: async REST API daemon and headless CI runner.
  • • Implementing mathematical CVSS v3.1 vector calculation algorithms, structured SARIF reporting, and standard CycloneDX 1.5 SBOM generation without external bloat.
  • • Rigorous software assurance discipline: 91% test coverage with Pytest (74 tests), strict static type checking with Mypy, Ruff linting, and 0 known vulnerabilities validated by `pip-audit`.
Technologies:
Python FastAPI Gitleaks TOML OSV Batch API CycloneDX 1.5 SARIF 2.1.0 GitHub Actions Pytest SQLAlchemy
Containers & Runtime v0.1.0 · 71 Tests (100% rules cov) · Active Release

Runtime container security auditing engine for Docker with native SARIF 2.1.0 reporting

Demostración técnica de DockerWard

Problem Statement

Static image scanners (such as Trivy or Grype) detect package CVEs at build time but remain completely blind to runtime execution: a vulnerability-free image becomes an immediate host compromise vector if executed with --privileged, a bind-mounted Docker socket, unconstrained cgroups, or disabled seccomp syscall filters.

Key Architecture Decisions

  • • Decoupled Docker Engine API collector: streams runtime telemetry over Unix domain sockets into typed Pydantic v2 models without shell wrapping or CLI subprocess dependencies.
  • • Modular CIS policy engine: evaluates 6 core rules featuring dynamic severity (differentiating read-write vs read-only socket exposure) and granular findings for memory, CPU, and PIDs.
  • • Compliant OASIS SARIF v2.1.0 exporter: integrates runtime findings directly into GitHub Security / Code Scanning dashboards complete with CVSS scores, technical impact, and remediation steps.
  • • CI/CD quality gate enforcement: configurable --fail-on flag returning standardized exit codes to fail builds or deployment pipelines upon detecting CRITICAL or HIGH misconfigurations.

Technical Challenges & Learnings

  • • Deep practical mastery of Linux kernel isolation primitives: unmapped user namespaces (UID 0 host inheritance), cgroups v1/v2 ceilings (mitigating OOM kills and fork-bomb denial-of-service via pids.max), capability bounding sets, and seccomp BPF syscall firewalls.
  • • Disciplined automated security testing: 71 unit and integration tests delivering 100% coverage on rules, backed by a reproducible 3-container testbed (privileged, exposed, and hardened control).
  • • Translating low-level container runtime state into multi-format developer tooling (Rich terminal tables, machine-readable JSON, and enterprise SARIF).
Technologies:
Python 3.12+ Docker Engine API Linux Kernel SARIF 2.1.0 Pydantic v2 Rich CLI Pytest
Cryptography & Anti-Surveillance v2.5.0 · 28 Pytest Tests · 12 Vitest Tests · Zero-Persistence RAM

Military-grade ephemeral messaging suite with native Zero-Knowledge Blind Relay, biometric voice scrambling, LSB steganography, and Android app with FLAG_SECURE

Demostración técnica de Chat Anónimo v2.5 — Privacy & Anti-Surveillance Suite

Problem Statement

Mainstream messaging platforms (WhatsApp, Telegram, Signal) compromise user sovereignty by mandating phone numbers, storing message histories on cloud servers, or harvesting vast communication metadata. Furthermore, standard E2EE tools lack defenses against direct physical coercion, forensic metadata leakage in attachments, biometric voiceprint profiling, or passive ISP traffic analysis.

Key Architecture Decisions

  • • Zero-Knowledge Blind Relay Architecture: The FastAPI server is technically incapable of decrypting frames, storing messages, or retaining keys (formally proven in test_server_inability.py); all cryptography is strictly isolated in volatile client RAM without disk storage.
  • • Anti-Forensic Defenses & Duress Decoy Room: In the event of physical extortion or coercion, entering PIN 9999, typing /duress, or pressing Ctrl+Shift+D triggers an instant in-memory key wipe and displays an innocent, fully functional university study group room.
  • • Deep Metadata Scrubber & SHA-256 Hash Masking: Every attached image or file is stripped in memory of EXIF metadata, GPS coordinates, and camera device serials, replacing the filename with a cryptographic hash before transmission.
  • • Real-Time Biometric Voice Scrambler: Web Audio API engine modulating vocal formants and pitch (Deep Pitch, Helium, Cyborg, Whisper) prior to encoding and encryption, defeating forensic acoustic identification and voiceprint profiling.
  • • View-Once Ephemeral Media & Self-Scrubbing Clipboard: Media viewer with 7-second countdown, automatic anti-capture blur upon losing focus, and irreversible blob destruction; operating system clipboard auto-wipes after 30 seconds.
  • • LSB Image Steganography & BIP-39 Passphrases: Capacity to inject confidential payloads into lowest-significant bits of carrier PNG photos, and back up 256-bit symmetric room keys using standard 24-word BIP-39 mnemonics with SHA-256 checksum verification.
  • • Native Android App with OS-Level FLAG_SECURE: Kernel-level protection blocking hardware screenshots (Power + Vol-), screen recording malware, and task switcher snapshots, reinforced with User-Agent header spoofing.

Technical Challenges & Learnings

  • • Protocol engineering with mathematical proof of technical inability on the relay intermediary (Blind Relay).
  • • Design of a strict fail-closed in-RAM lifecycle revoking Blob Object URLs and zeroing symmetric keys upon panic or disconnect.
  • • Asymmetric key agreement via ECDH P-256 with visual 4-word Short Authentication String (SAS) for mathematical Man-In-The-Middle (MITM) defense.
  • • Mitigation of side-channel attacks, acoustic voice fingerprinting, and packet-length statistical traffic analysis through periodic decoy traffic.
Technologies:
WebCrypto API (AES-256-GCM) ECDH (P-256) & HKDF Web Audio API (Voice Scrambler) LSB Image Steganography BIP-39 Mnemonic Derivation Android Native (Capacitor FLAG_SECURE) FastAPI & WebSockets React 19 & TypeScript Strict TailwindCSS v4 MediaRecorder E2EE Pytest (28 Suites) Vitest (12 Suites)
Perimeter & EASM v0.1.0 · 86 Tests (100%) · 0 CVEs · Hardened Non-Root

High-performance backend API for perimeter security auditing and External Attack Surface Management (EASM)

Demostración técnica de SecuScan API

Problem Statement

Organizations face an expanding internet-facing attack surface (orphaned subdomains, exposed services without strong encryption, permissive HTTP headers, and insecure DNS records vulnerable to email spoofing). Most existing EASM tools are expensive enterprise SaaS or intrusive scripts that lack protection against SSRF, DNS rebinding, and unauthorized scanning.

Key Architecture Decisions

  • • Passive Subdomain Discovery: Maps external attack surface by querying Certificate Transparency logs (`crt.sh`) without transmitting intrusive traffic to the target.
  • • TLS/SSL Deep Inspection: Strict detection of obsolete protocols (`TLS 1.0`, `1.1`, `SSLv3`), weak cipher suites, certificate trust chains, and expiration telemetry.
  • • Defensive HTTP Header Auditing: Rigorous compliance validation of modern security directives (`HSTS`, `CSP`, `X-Frame-Options`, `X-Content-Type-Options`, and `Referrer-Policy`).
  • • DNS Email Hygiene & Anti-Spoofing: Syntax and policy inspection for `SPF` (flagging permissive `~all` or `?all`), `DMARC` (`p=reject`/`quarantine`), and `DKIM` selectors.
  • • Async Port Scanner with Anti-DNS Rebinding: Pre-resolves IP addresses and binds direct TCP sockets at the IP level to eradicate DNS rebinding attack vectors.
  • • Anti-SSRF Perimeter Hardening: HTTP client with hop-by-hop inspection across 3xx redirects, blocking private ranges (RFC 1918) and cloud metadata services (`169.254.169.254`).
  • • Cryptographic Domain Ownership Handshake: Requires random TXT token verification (`_secuscan-challenge.<domain>`) before scans can be triggered on any target.
  • • Security Posture Score Engine: Weighted mathematical scoring (0-100) with transparent risk letter grades (`A+` to `F`) and itemized deduction matrices.
  • • Dual Executive & Standard Reporting: Executive Markdown summaries and native OASIS SARIF 2.1.0 exporter for GitHub Code Scanning and DefectDojo.
  • • Container Hardening: Docker deployment running as unprivileged `appuser` (UID 1000) with PostgreSQL isolated within an internal private virtual network.

Technical Challenges & Learnings

  • • Engineering critical perimeter defenses: robust SSRF neutralization in async HTTP clients and low-level socket handling to mitigate DNS rebinding.
  • • Architecting non-intrusive asset recon via Certificate Transparency and designing multi-factor security scoring algorithms.
  • • Standardizing vulnerability findings under OASIS SARIF 2.1.0 and upholding disciplined test automation: 86 Pytest suites (100% pass) and zero CVE dependencies.
Technologies:
Python 3.12 FastAPI EASM & DNS Security TLS/SSL Deep Inspection Anti-SSRF & DNS Rebinding SARIF 2.1.0 PostgreSQL & SQLAlchemy Docker Hardened Pytest (86 Tests)

Experience

Technical track record and development contributions

Independent Systems & Software Development

Software Developer

Building and maintaining infrastructure automation tools, Linux system hardening scripts with Bash, and lightweight Python backend services prioritizing reliability and predictability.

Key responsibilities & accomplishments

  • • Authored and actively maintained ArchForge, a modular post-install and hardening toolkit for Arch Linux with automated backup and dry-run modes.
  • • Built CLI tooling and lightweight automation services to streamline developer workstation provisioning and server tasks.
  • • Configured reproducible Linux environments using dotfiles, systemd units, and network security policies.
Linux Bash Python Git systemd

Open Source Contributions on GitHub

Open Source Developer

Publishing and maintaining public repositories, writing rigorous technical documentation, and applying software engineering workflows.

Key responsibilities & accomplishments

  • • Maintained publicly accessible codebases with detailed setup guides and configuration manifests.
  • • Enforced disciplined commit conventions, release notes, and structured issue tracking.
  • • Engineered sanity check routines to guarantee compatibility across Arch-based systems.
Git GitHub Markdown Shell Scripting

Technical Skills

Tools and technologies with proven hands-on experience in production

Systems & Automation

  • Linux / Arch Linux Administración, configuración y uso diario
  • Bash & Shell Scripting Scripts modulares, automatización e idempotencia
  • systemd Gestión de servicios, units, timers y daemons
  • nftables & Firewall Reglas básicas de filtrado de paquetes y seguridad
  • Linux CLI & Utilities grep, sed, awk, find, coreutils, ssh

Backend & Databases

  • Python Lógica backend, utilidades de automatización y scripts
  • APIs REST Diseño de endpoints HTTP y contratos JSON
  • Bases de Datos Relacionales SQL, consultas estructuradas, MySQL / PostgreSQL

Tools & Version Control

  • Git Control de versiones, branches, rebasing, commits semánticos
  • GitHub Gestión de repositorios abiertos, issues y releases
  • Entornos Reproducibles Dotfiles y configuración estandarizada

Education & Certifications

Academic education and specialized continuous learning programs

En curso

Systems Engineering (in progress)

University in Colombia

Undergraduate curriculum covering algorithms, computer architecture, computer networks, and operating systems.

2024

Google Cybersecurity Professional Certificate

Google (via Coursera)

Foundations in network security, Linux hardening, threat mitigation, and SQL for audit and incident analysis.

2023

Linux Environment Hardening & Customization

Hack4U (Savitar)

Advanced tuning and securing of Unix-based workstations, dotfiles orchestration, and scripting workflows.

2023

Oracle Next Education — Backend Specialization

Oracle & Alura Latam

Intensive training in backend engineering, software logic, relational databases, and agile team practices.

Get in Touch

No spammy forms or friction. Reach me directly via email or professional profiles.

h3n.eth@gmail.com

I typically reply within 24-48 hours. Always open to discussing Linux systems, open source tooling, and new projects.

Send an Email